
Yes, healthcare organizations can use electronic signatures under HIPAA, provided the workflow protects PHI and meets ESIGN Act and UETA enforceability standards. Before you sign off on any vendor or workflow, confirm four things right now: a signed Business Associate Agreement, a timestamped audit trail, authentication strong enough for the document type, and the ability to export records intact. Skip any one of those and you’re carrying real regulatory risk, not just an inconvenience.
TL;DR:
- Enforceability of electronic signatures relies on laws like ESIGN and UETA, but HIPAA requires additional safeguards such as audit trails and authentication for PHI documents.
- Different document types need varying levels of signature security, with controlled substances and FDA submissions requiring cryptographic or PKI-backed digital signatures.
- For healthcare workflows, identity verification, audit logging, and secure record export are essential across all stages, from intake to clinical trials.
- Vendors must provide detailed controls in authentication, integrity, encryption, and audit logging, with audit trails including timestamps, actor identity, version history, and protected export files.
- Medical records must be retained for at least six years, including full audit trails, certificate chains, and export archives, to ensure verifiability and regulatory compliance.
Table of Contents
- Electronic Signature Healthcare Compliance: The Legal Baseline
- Which Type Of E-Signature Fits Each Document?
- Where E-Signatures Fit Across Admissions And Care
- What Technical Controls Should You Require From A Vendor?
- How Long Should You Keep Signed Records, And What Goes In The File?
- Vendor Risk Assessment: What To Verify Before You Sign
- Building Your Deployment Checklist For Admissions And Intake
- Which Compliance Steps Come First When Resources Are Limited?
- A Smarter Way To Handle Signed Documents During Intake
- Sources
- FAQ
Electronic Signature Healthcare Compliance: The Legal Baseline
Two federal laws make electronic signatures enforceable in the United States: the ESIGN Act and the Uniform Electronic Transactions Act. Neither one mentions healthcare specifically. They establish the general rule that an electronic signature carries the same legal weight as ink on paper, as long as the signer intended to sign, consented to do business electronically, and can be reliably attributed to the record.
That’s the floor. HIPAA builds a second story on top of it. Once a document contains protected health information, the Security Rule and Privacy Rule kick in, and enforceability alone isn’t enough. You also need confidentiality, integrity, and an audit trail that proves who signed what, when, and from where. The HIPAA Journal’s analysis of e-signature use confirms that e-signatures are permitted under HIPAA, but only when the platform’s mechanisms guarantee signer authenticity, message integrity, and non-repudiation.
HIPAA’s technical safeguards, laid out across 45 CFR §§164.300 through 164.312, apply to any electronic system touching ePHI, including your signature platform. That means access controls, audit controls, and integrity checks aren’t optional add-ons. They’re baseline requirements your compliance team needs to verify before go-live.
A few practical points to keep in front of your team as you evaluate vendors or build internal policy:
- ESIGN and UETA govern enforceability. They confirm the signature holds up legally, not that PHI is protected.
- HIPAA governs PHI handling. Confidentiality, access control, and audit logging sit on top of the enforceability layer.
- State law can add friction. A handful of states carve out exceptions for specific document types (wills, certain court filings), so don’t assume federal preemption covers every form in your intake stack.
- Document-specific rules can override the general standard. Controlled-substance prescribing and certain FDA-regulated submissions require additional controls beyond a standard e-signature capture.
None of this means you need a lawyer signing off on every intake form. It means your vendor contract and your internal workflow both need to answer the same question: can we prove, later, exactly who signed this and that nobody altered it afterward?
Which Type Of E-Signature Fits Each Document?
Not every signature needs the same horsepower. A simple electronic signature, click to sign, typed name, or drawn signature, captures intent and consent but relies on the platform’s audit trail for proof of identity. A digital signature adds a cryptographic layer: public key infrastructure (PKI) binds the signature to a certificate, making any post-signature alteration detectable.
The gap between the two comes down to three things: identity proofing strength, non-repudiation, and long-term validation. A simple e-signature on a discharge instruction sheet is usually fine. A regulatory submission under FDA 21 CFR Part 11, or a controlled-substance e-prescription under DEA EPCS rules, demands stronger proof. ISO 17090-4:2026 defines the PKI profiles and long-term signature formats healthcare organizations should reference when a document needs to remain verifiable years after it’s signed.
Match assurance level to document risk:
- Simple e-signature: intake forms, routine consents, discharge instructions.
- Digital signature with PKI: clinical trial consents, FDA-regulated submissions, high-value contracts.
- EPCS-certified signing: any controlled-substance e-prescribing workflow, no exceptions.
Pro Tip: When exporting signed records for long-term storage, include the full certificate chain and OCSP/CRL responses alongside the document. Without them, a digital signature can become unverifiable the moment the issuing certificate expires, even if the signature itself was valid at signing time.
Where E-Signatures Fit Across Admissions And Care
The right configuration changes based on where in the care journey the signature happens. Applying one blanket setup across intake, bedside consent, and clinical trials is how compliance gaps show up during an audit.
- Pre-visit intake and registration. Minimize PHI fields on the form itself, and link the completed packet to the EHR record immediately rather than storing it as a standalone file. Build in identity checks so a form can’t be completed by someone impersonating the patient.
- In-clinic signing on kiosks or tablets. Lock the device to the signing application, secure the local network, and set the platform to export a completed audit trail the moment the session ends, not at the end of the day.
- Bedside informed consent. Verify identity before presenting the consent document, and capture clinician or witness attestation alongside the patient’s signature. The timestamped audit trail here is often the single piece of evidence that resolves a later dispute.
- Discharge instructions and referrals. Archive the signed packet with role-based access controls and version history, since referral documents frequently move between facilities and need a clear chain of custody. Smartadmissions covers this handoff in more detail in its referral documentation guide.
- Clinical trial consents. These need the highest assurance tier: identity-verified signing, a complete evidentiary package, and documentation that satisfies FDA 21 CFR Part 11 reviewers, not just HIPAA auditors.
What Technical Controls Should You Require From A Vendor?
Ask any e-signature vendor to walk you through four categories before you sign a contract: authentication, integrity, encryption, and audit logging. If they can’t answer specifically, that’s your answer.
Authentication strength should scale with the document. One-time passcode (OTP) verification is reasonable for routine intake paperwork. Higher-risk documents, consent for a clinical trial or anything touching controlled substances, need identity proofing or PKI-backed digital signatures instead of a simple code sent by text.
Integrity and tamper evidence come from cryptographic signing, hashed document storage, and reliable time-stamping. A document that can be edited after signing without detection fails HIPAA’s integrity requirement outright, regardless of how the signature itself was captured.
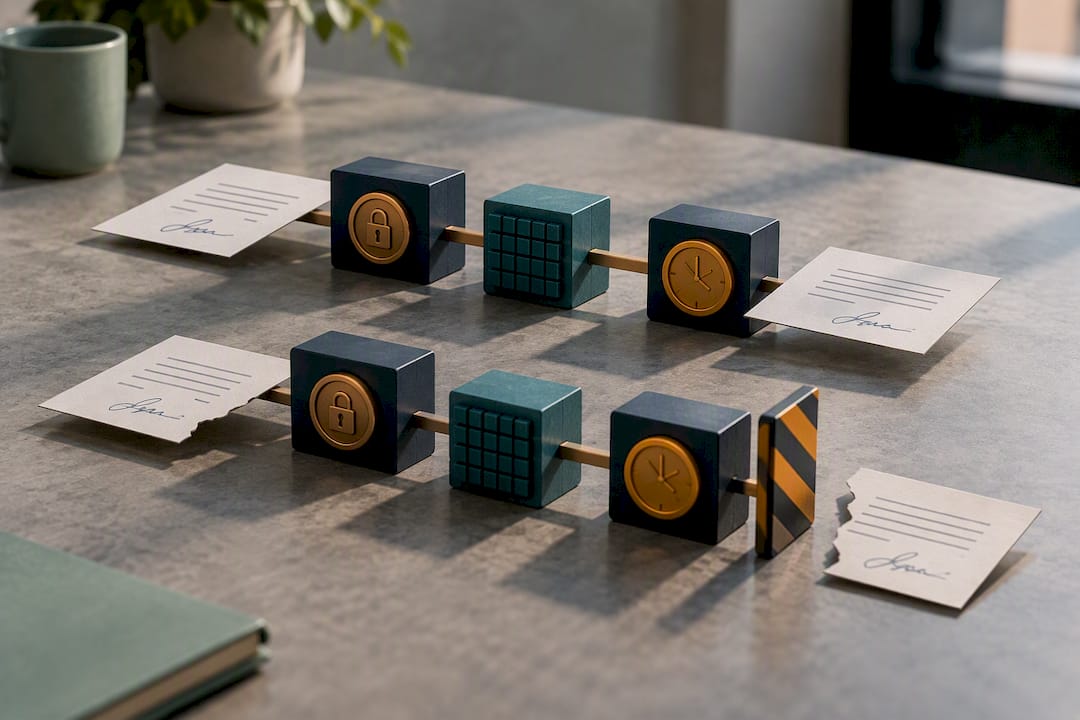
Encryption needs to cover both states: TLS 1.2 or 1.3 in transit, AES-256 at rest. Ask how the vendor manages encryption keys, not just whether encryption exists, since weak key management undermines strong encryption.
The audit trail is where most disputes get settled. According to the HIPAA Journal, non-repudiation in a healthcare signing workflow depends almost entirely on a timestamped log that captures actor identity, exact time, action taken, IP address, and document version. Require that your vendor’s audit trail:
- Records actor identity tied to a verified account, not just a name field.
- Logs the precise timestamp and IP address for every action, including views and downloads.
- Tracks document version so you can prove nothing changed between signing and archival.
- Exports as a standalone, portable file that doesn’t require the vendor’s platform to open or verify.
- Stays protected from deletion or alteration, even by administrators, without its own separate log entry.
A signature platform that can’t produce this package on request during an HHS FAQ on electronic BAAs points out that covered entities remain responsible for verifying access and audit controls even when a vendor handles the technical implementation. The obligation doesn’t transfer just because you outsourced the tool.
How Long Should You Keep Signed Records, And What Goes In The File?
HIPAA’s baseline retention rule requires covered entities to keep documentation for six years from creation or last effective date, whichever is later. Many healthcare organizations extend that internally, particularly for pediatric records or anything tied to litigation risk, so check your own retention policy against the six-year floor rather than assuming it’s the ceiling.
A complete evidentiary package, the file you’d hand to an OCR investigator or opposing counsel in a dispute, needs more than the signed PDF. It should include:
- The final signed document, with version history intact.
- The full audit trail, timestamped and unedited.
- The certificate chain, if a digital signature was used.
- OCSP or CRL responses confirming the certificate’s validity status at signing time.
- A record of the BAA covering the vendor that stored or processed the document.
Build export and archiving into your operational calendar rather than treating it as a one-time setup task. Schedule regular exports to an immutable archive separate from your live signing platform, and periodically test that you can actually restore a record from that archive. An archive nobody has tested is a liability disguised as a safeguard. Smartadmissions’ audit trail requirements guide breaks down the specific fields compliance teams should confirm before relying on any export.
Vendor Risk Assessment: What To Verify Before You Sign
A signed BAA is non-negotiable the moment a third-party vendor stores or transmits PHI on your behalf. The ESIGN Act makes the electronic signature itself enforceable, but it says nothing about PHI protection, which is entirely HIPAA’s domain and entirely your responsibility to verify.
- Confirm the BAA covers the actual workflow. Some vendors sign a generic BAA that doesn’t specifically address signature storage or audit trail custody. Read the scope language, not just the signature block.
- Request SOC 2 or equivalent security attestations. These document the vendor’s internal controls, not just their marketing claims about encryption.
- Run a threat model specific to signing. Misdelivery (a form sent to the wrong patient), account takeover, and template tampering are the three failure modes that show up most often in healthcare signing workflows.
- Lock templates and minimize PHI fields. Every field you don’t need on a form is a field you don’t have to protect if the form leaks.
- Set role-based sending permissions. Front-desk staff sending consent forms shouldn’t have the same system access as compliance staff pulling audit exports.
Pro Tip: Run a 30-day pilot with a single document type before rolling a new signature workflow across every intake form. It’s far easier to catch a misconfigured audit export or a missing BAA clause on one form type than to discover it after six months of signed discharge packets are already in the wrong storage bucket.
Building Your Deployment Checklist For Admissions And Intake
Rolling out electronic signature healthcare workflows across an admissions department works best as a staged process, not a single flip of a switch.
- Inventory every document that gets signed, from intake through discharge, and assign each one a required assurance level based on its risk. Smartadmissions’ intake documentation guide is a useful starting template for this step.
- Map each signed document to its target EHR field so signed packets land in the right chart section automatically instead of sitting in a separate folder someone has to reconcile manually.
- Set up API or webhook logging between your signature platform and your storage system, so every signature event triggers an automatic, timestamped record.
- Build role-based permissions and lock templates before training a single staff member, so nobody can improvise a workaround once the workflow goes live.
- Pilot with one document type, review the audit export end to end, and confirm it contains everything an auditor would expect.
- Schedule recurring audits and test restores after go-live, and designate a specific contact person for vendor incident response.
Pro Tip: Treat your first audit export like a fire drill. Pull a record, hand it to someone outside the project team, and ask them to verify who signed it and when without any help from you. If they can’t, your export format needs work before a real auditor finds the same gap.
Which Compliance Steps Come First When Resources Are Limited?
If your team can’t fix everything at once, fix the BAA and the audit trail before anything else. A missing BAA is the single fastest way to turn a routine signature workflow into a reportable incident, and a weak or incomplete audit trail is what makes every other control impossible to prove after the fact.
Authentication strength matters, but it’s the second priority, not the first. A well-documented workflow with a simple e-signature and airtight audit logging will hold up better under scrutiny than a sophisticated PKI setup with sloppy record keeping. Templates and automation reduce the human error that creates most real-world gaps, misdelivered forms, incomplete fields, missing witness attestations, far more reliably than upgrading signature technology alone.
Reserve PKI and digital signatures for the documents that genuinely require them: clinical trials, FDA submissions, controlled-substance prescribing. Everywhere else, a well-configured workflow with strong authentication and a clean audit trail does the job without the added operational overhead. When a document’s risk profile is unclear, that’s the moment to loop in legal or IT, not after the workflow is already live.
— Harry
A Smarter Way To Handle Signed Documents During Intake
Getting the signature right is only half the job. The other half is making sure every signed intake packet, referral, and consent form actually lands where it belongs without someone manually re-entering data into the EHR. Smartadmissions was built by people who understand healthcare documentation, and it centralizes template management, automates the export of signed records and their audit logs, and integrates with existing EMR and insurance systems to keep chain of custody intact from the moment a form is signed.
Facilities using automated referral workflows report improved efficiency because admissions staff aren’t chasing paperwork across multiple systems. Onboarding is designed to be efficient, and the platform is supported by a guarantee aiming to demonstrate a rapid return on investment. Check the Monthly or Annually pricing plans and see whether a faster, better-documented intake process is worth testing at your facility this quarter.
This article is general information, not a substitute for advice from a qualified doctor. Consult a qualified healthcare professional about your own circumstances before acting on anything here.
Sources
- Can E-Signatures Be Used Under HIPAA Rules?
- HHS FAQ: Business associate contracts in electronic form acceptable?
- Electronic Signatures in Global and National Commerce Act (ESIGN Act)
- 45 CFR (selected regulatory references)
- ISO 17090-4:2026 – Digital signatures for healthcare documents
FAQ
Are Electronic Signatures HIPAA Compliant?
Yes, electronic signatures are HIPAA compliant when the platform protects PHI through access controls, encryption, and a timestamped audit trail, and when a signed BAA is in place with any third-party vendor. The HIPAA Journal confirms this requires authenticity, integrity, and non-repudiation mechanisms, not just a checkbox agreement.
What Are The Three Types Of Electronic Signatures?
The three general tiers are simple electronic signatures (typed name or click to sign), advanced electronic signatures (tied to identity verification and tamper evidence), and qualified or digital signatures using PKI-backed certificates. Healthcare organizations should match the tier to document risk, reserving PKI-based signing for regulated submissions and controlled-substance prescribing.
What Are The Rules For Electronic Signatures In Healthcare?
Electronic signatures must meet the enforceability standards in the ESIGN Act, covering signer intent, consent, and attribution, while also satisfying HIPAA’s Security Rule requirements for confidentiality, integrity, and audit controls under 45 CFR. Certain documents, like controlled-substance prescriptions or FDA-regulated submissions, carry additional sector-specific rules on top of those baseline requirements.
Is DocuSign HIPAA Compliant In Healthcare?
Whether any e-signature platform is HIPAA compliant depends on configuration, not the product name alone: a signed BAA, properly configured access controls, and an exportable audit trail all have to be in place. A platform’s general enforceability under the ESIGN Act doesn’t automatically mean it’s configured correctly for PHI, so healthcare organizations need to verify the BAA and technical safeguards directly with any vendor before relying on it for signed medical documents.
Does Smartadmissions Handle E-Signature Workflows Directly?
Smartadmissions focuses on referral and admissions automation, integrating with existing EMR and insurance systems while centralizing document templates and automating the export of signed records and audit logs. Pricing details are available on the Smartadmissions pricing page, where current Monthly and Annually plans are listed.